




01
Human-Led Testing
Experienced security researchers validate vulnerabilities, uncover attack paths, and identify risks automated scanners miss.
EXPERT-LED OFFENSIVE SECURITY
Qualysec brings expert-led testing, vulnerability validation and remediation guidance into a structured, ongoing security program, helping your team address risk as applications and infrastructure evolve.
BEYOND PENTESTING
Expert insight, AI and tools combine in a process-based approach to secure your enterprise.
Explore our testing approach
Experienced security researchers validate vulnerabilities, uncover attack paths, and identify risks automated scanners miss.
We test application workflows and business logic to identify realistic ways attackers could abuse systems.
We assess security across web, mobile, APIs, cloud, networks, IoT, AI systems, and enterprise environments.
Our reports align with 74+ security and compliance standards, including SOC 2, ISO 27001, PCI DSS, and more.
Our testers engage with your team to explain findings, shape fixes, and verify every remediation through retesting.
We follow OWASP, SANS, OSSTMM, ISSAF, PTES, NIST, CVSS, CWE, MITRE, and CIS standards.
Our Offensive Security Services
Every environment carries different risks, so our specialized pentesting services are shaped around yours, backed by expert guidance, clear evidence, and retesting that confirms each fix is complete.
We test web applications from single-page experiences to high-traffic platforms, including complex API and AI integrations.
We combine SAST and DAST to assess mobile apps across source code, runtime behavior and integrations.
We examine API architecture, authentication, data flows and integrations across the services powering your applications.
We test legacy applications with extensive API interactions, complex integrations and interconnected workflows.
We test Windows and Linux desktop applications across GUI, CLI, local components and connected services.
We review source code in any programming language for security flaws, exposed secrets and unsafe dependencies.
Client Testimonial
See why customers choose Qualysec and what they value about working with us.
The team demonstrated exceptional professionalism with their consistently short response times and strict adherence to the project schedule. Their professionalism was impressive.
Application Security Testing
Read case studyCompliance starts with real proof. We help you achieve every framework and regulation with reports built around what auditors need.
Explore All Compliance Requirements
YOUR PENETRATION TESTING ADVISOR
QUALYSEC’S PTaaS PLATFORM
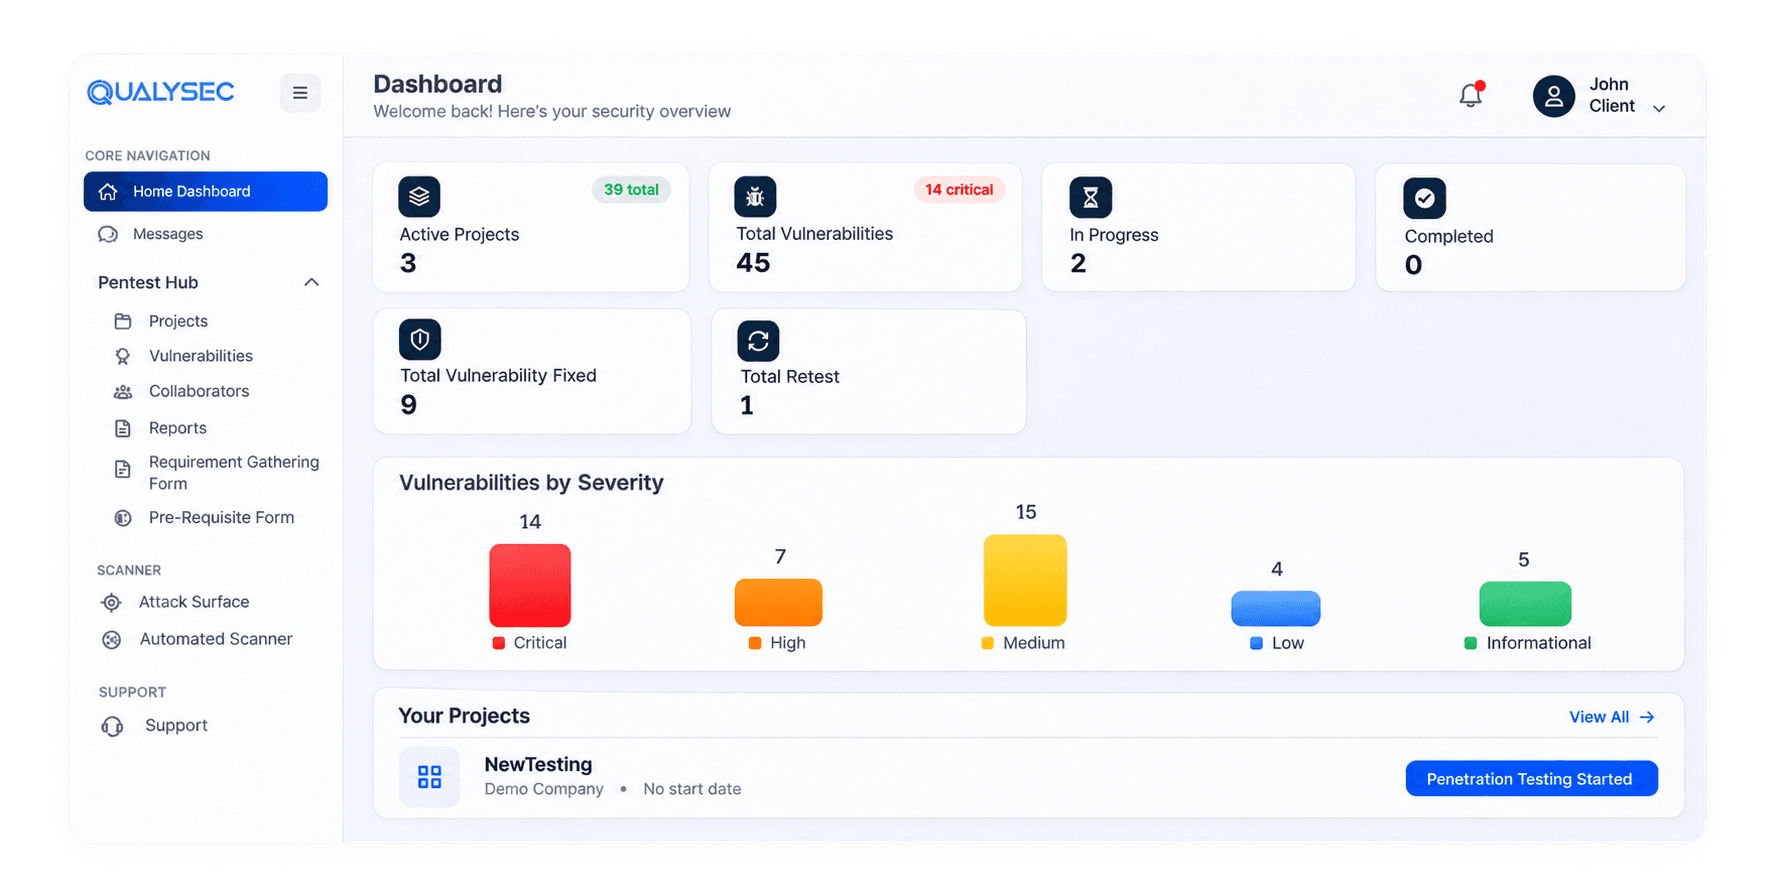
Qualysec’s PTaaS combines expert penetration testing with a live platform where your team reviews findings, assigns fixes, tracks progress and confirms remediation through retesting, without chasing updates.
Explore webinars, white papers, guides, and blogs to stay informed on the latest cybersecurity threats, trends, and best practices.
White Paper
White Paper
White Paper
Attackers never pause, so neither should you. Fill out the form and let’s build proactive security together, starting today.
sales@qualysec.com60,000+
Vulnerabilities identified
43+
Countries Served
3,700+
Security assessments
520+
Clients
6+
Years in cybersecurity
Explore webinars, white papers, guides, and blogs to stay informed on the latest cybersecurity threats, trends, and best practices.
White Paper
White Paper
White Paper